

Paper
James M. Acton, Ankit Panda
{
  "authors": [
    "James M. Acton"
  ],
  "type": "other",
  "centerAffiliationAll": "dc",
  "centers": [
    "Carnegie Endowment for International Peace"
  ],
  "collections": [],
  "englishNewsletterAll": "ctw",
  "nonEnglishNewsletterAll": "",
  "primaryCenter": "Carnegie Endowment for International Peace",
  "programAffiliation": "NPP",
  "programs": [
    "Nuclear Policy"
  ],
  "projects": [],
  "regions": [],
  "topics": [
    "Nuclear Policy",
    "Foreign Policy"
  ]
}
Source: Getty
The advent of cyber warfare exacerbates the risk that conventional wars could inadvertently lead to the use of nuclear weapons.
Source: Daedalus
Cyber weapons may be relatively new, but non-nuclear threats to nuclear weapons and their command, control, communication, and intelligence (C3I) systems are not. In fact, before the United States dropped the bomb on Hiroshima in August 1945–before it even conducted the world’s first nuclear test in July of that year–it had started to worry about non-nuclear threats to its nascent nuclear force, in particular, Japanese air defenses. As the Cold War developed, fears multiplied to encompass threats to almost every component of the United States’ nuclear forces and C3I systems. While these threats emanated primarily from Moscow’s nuclear forces, they were exacerbated by its improving non-nuclear capabilities, particularly in the final decade of the Cold War. A two-decade hiatus in worry following the Soviet Union’s collapse is now over; today, non-nuclear threats to U.S. nuclear C3I assets–in particular, the growing capability of Chinese and Russian antisatellite weapons–are a major concern.
The United States’ experience is the norm. All nuclear-armed states have felt, and continue to feel, similar concerns. Indeed, the last few decades have seen the emergence of new potential vulnerabilities–this time in cyberspace–as nuclear weapons and C3I systems have come to rely increasingly on digital technology. To be sure, the networks involved in nuclear operations are almost certainly among the most secure anywhere. Yet there is broad agreement among technical experts that perfect network security is “impossible.” As a result, the possibility of cyber interference with nuclear forces and C3I systems is real.
The full article is published in the Spring 2020 issue of Daedalus.
Jessica T. Mathews Chair, Co-director, Nuclear Policy Program
Acton holds the Jessica T. Mathews Chair and is co-director of the Nuclear Policy Program at the Carnegie Endowment for International Peace.
Recent Work
James M. Acton, Ankit Panda
James M. Acton
Carnegie does not take institutional positions on public policy issues; the views represented herein are those of the author(s) and do not necessarily reflect the views of Carnegie, its staff, or its trustees.
The Bureau of Industry and Security needs to adjust its focus and practices to maintain its position as the U.S. government’s primary champion of international technological competition.
Geoffrey Irving
European Commission President Ursula von der Leyen is about to give her annual address on the state of the EU. Here’s what she won’t—but should—say.
Rym Momtaz

The books, podcasts, and films that explain the world it made.
Andrew Leber
U.S. trading partners in Asia are closely watching the dispute for signs of how it may affect their own interests.
Barbara Weisel
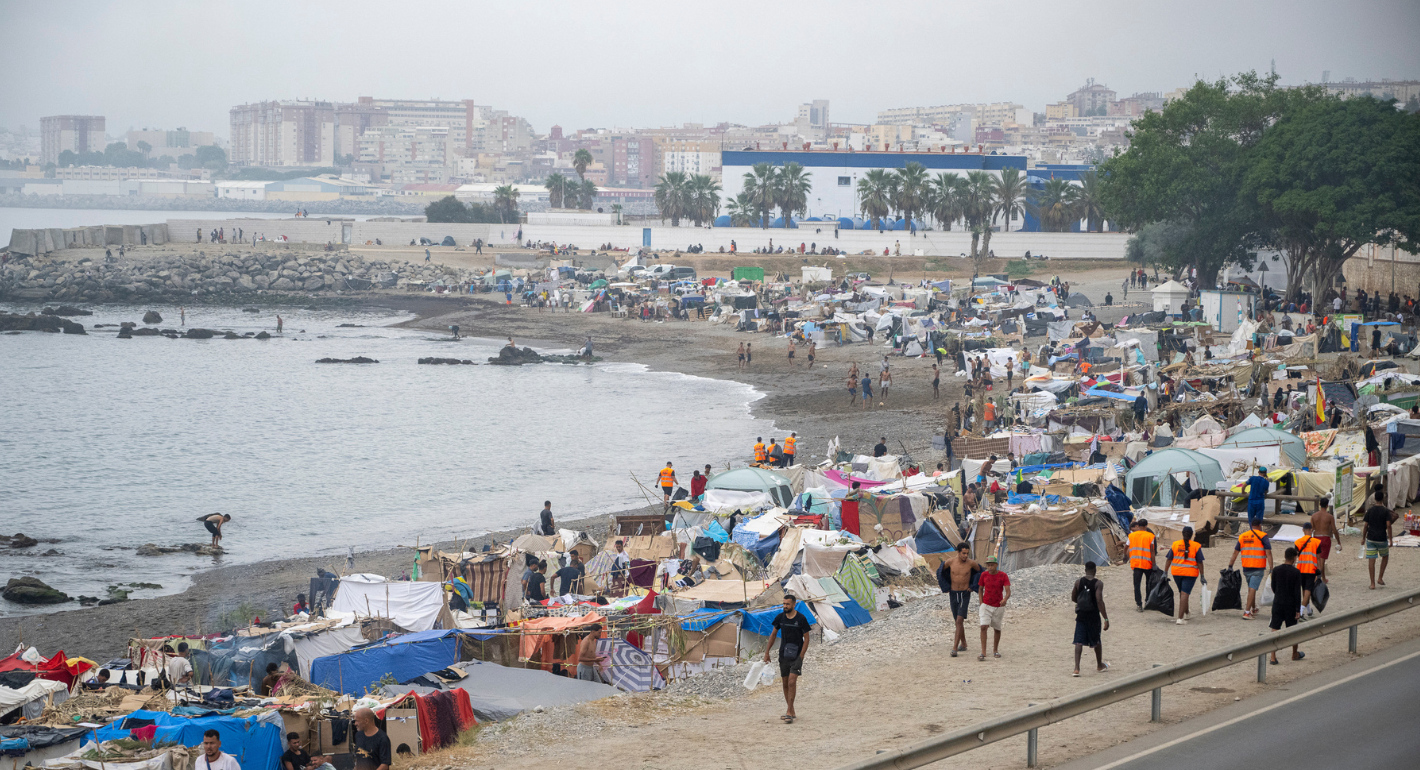
The aftermath of the Ceuta crisis shows Europe has drawn the wrong lessons. Rather than doubling down on failed migration policies, the EU needs to address the underlying roots of such episodes.
Richard Youngs